# FedRAMP Deliverables
Representing the FedRAMP Certification Package Overview (CPO) and Security Decision Record (SDO) in OSCAL and translating between OSCAL and the FedRAMP-published bespoke schema. Although also FedRAMP Artifacts, [KSIs ](https://patterns.rufrisk.com/books/key-security-indicators-ksis)are receiving separate focus.
# CR26 Deliverables Overview
DRAFT - PLEASE PROVIDE INPUT
The following is an overview of how the FedRAMP CR26 Deliverables are represented using OSCAL models.
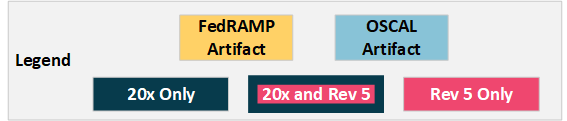
[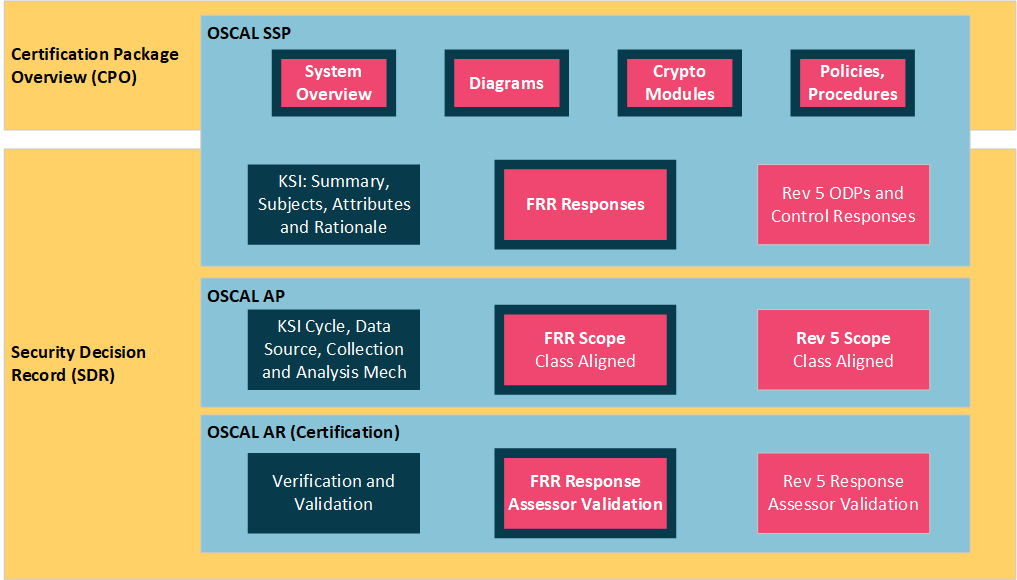](https://patterns.rufrisk.com/uploads/images/gallery/2026-09/cr26-cpo-and-sdr.png)
# Certification Package Overview (CPO):
- System details are very similar to legacy SSP front-matter.
- Requires summary of assessment details found in SDR. This summary is generated from that data.
# Security Decision Record (SDR):
- CSP responds to all applicable FedRAMP Rules (FRRs) for both 20X and Rev 5 paths.
- 20X Path: CSP also defines KSIs Rev 5 Path: CSP also responds to controls.
- Assessor validates all CSP responses (FRR and either KSI definitions or Rev 5 controls).
---