FedRAMP TFG CR26 Efforts
CR26 Overview
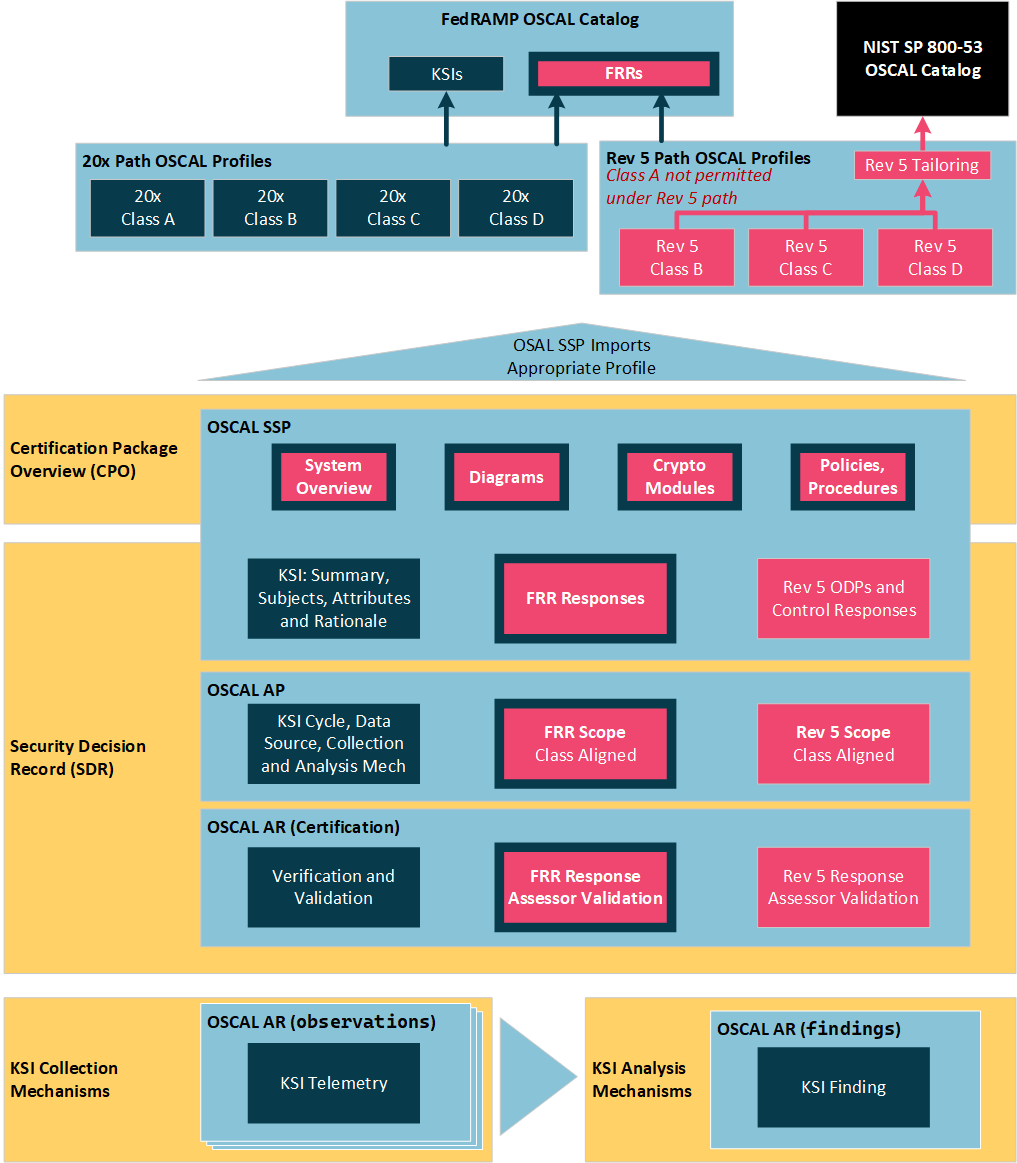
The following is a depiction of how the FedRAMP Published Artifacts, Deliverables and KSI Automation fit together under FedRAMP Consolidated Rules 2026 (CR26).
The effort to map these in detail and produce related OSCAL content is broken down into multiple Workstreams.

Workstreams
The OSCAL Foundation's FedRAMP TFG is currently focused on three workstreams realted to the FedRAMP PMO's Consolidated Rules 2026 (CR26):
-
FedRAMP Published Artifacts: Representation of the FedRAPM Rules (FRRs), Key Security Indicator (KSI) definitions, and Rev 5 Baselines in OSCAL Format. Intended to include capabilities for converting FedRAMP-published JSON to OSCAL.
-
FedRAMP Deliverables: Representaiton of the Certification Package Overview (CPO) and Security Decision Records (SDRs) in OSCAL Format. Possibly including capabilities for converting OSCAL to the FedRAMP-published schema files for these artifacts.
-
KSI Automation: Representaiton, process support and recommended practices for KSI source definitions, KSI automated collection tooling, KSI telemetry representation in OSCAL, and KSI-driven compliance/risk reporting in OSCAL.
-
Vulnerability Evaluation and Reporting (VER): Representation of vulnerability reporting in OSCAL.