KSI Example
The OSCAL Foundation's FedRAMP TFG elected to focus on [KSI-IAM-AAM] Identity and Access Management: Automated Account Management.
This is an example of how KSIs could be implemented in OSCAL. It does not necessary reflect exactly what should be collected or how.
KSI-IAM-AAM
The lifecycle and privileges of all accounts, roles, and groups are securely managed using automation.
The
 - lifecycle and
    - privileges of
 - all accounts, roles, and groups
 - are securely managed
   - using automation.
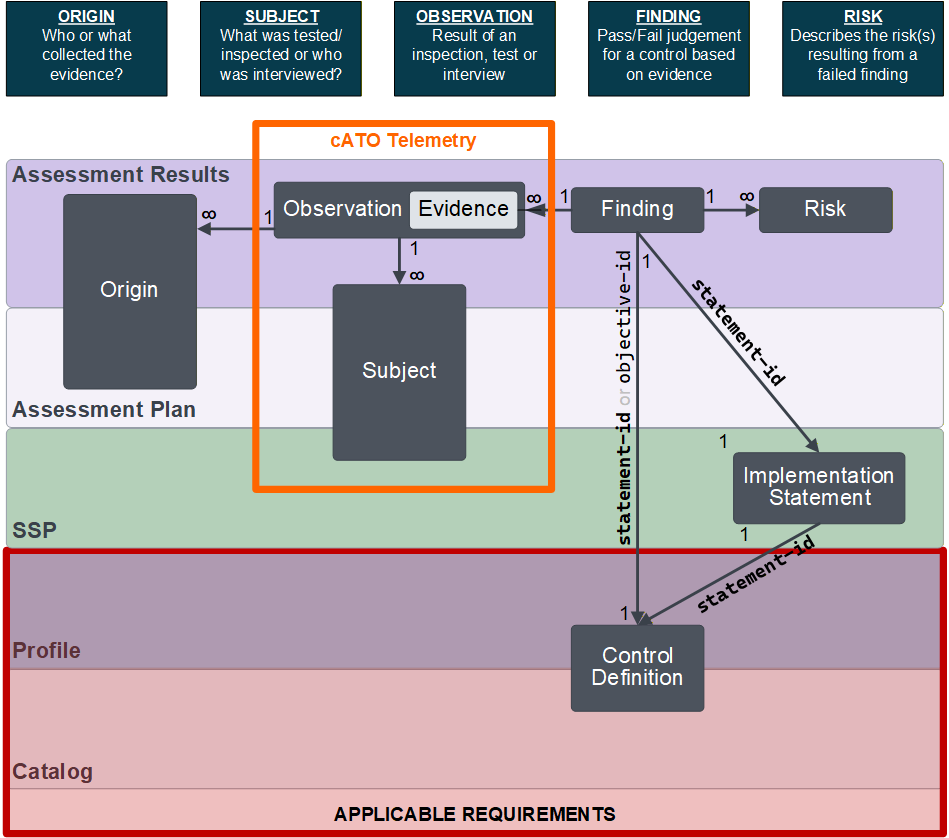
Subjects
- Identity and Access Management Process
Evidence
-
For EVERY [ account (human and machine) | role | group ] , process artifacts (logs?) exist for that account's:
- creation
- privlige modification (requires some kind of manager approval)
- disablement; and
- deletion.
-
Creation is triggered by an appropriate event:
-
privilege escalation is triggered by an appropriate event
-
privilege reduction is triggered by an appropriate event
-
disablement is triggered by an appropriate event (offboarding, lack of use)
-
deletion is triggered by an appropriate event
Appropriate Triggers Might Include
- external process (onboarding, offboarding, contractor onboarding)
- approval by authorized individual or role
- signing of some license agreement, RoB, etc.
Questions to Answer
- What does telemetry look like, vs point-in-time?